Thinking out loud, one build at a time.
Devlogs, notes and the occasional rant. The ideas that stick around long enough to be written down eventually find their way here.
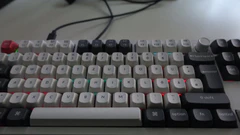
- Tina taught her keyboard to rainEvery key press is a raindrop. A damped wave equation in Q16 on a 40 MHz Realtek chip and the two weeks it took three friends to get there.15 min#hardware
- Wrong Boot (codename: wrong8007)A programmable dead man's switch for Linux, living entirely in kernel space.13 min#personal
- Personal challenge for 2023: OrganizePersonal challenge for 2023, organizing. I know.2 min#year-in-review
- Do things that eventually scalePaul Graham's legendary advice is often misunderstood. Here's my take on what it really means.5 min#startups
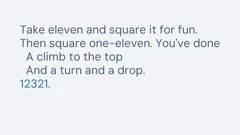
- Introducing PalindrickA limerick whose last line reads the same backwards.3 min#writing
- Have a jalebi.An experiment in spirals, sine waves, and handcrafted chaos in C.1 min#creative-coding
- Sensitive Data Exposure over *.unesco.org, thanks to OptionsBleed for low-hanging fruitOptions Bleed is a use after free error in Apache HTTP which helped in seeking the direct leak of sensitive data through a misconfigured server-status module.1 min#security
- Address bar spoofing in Firefox Lite for Android ...and the idiocy that followedFirefox Lite 1.9.2 for Android and earlier suffer from Address Bar Spoofing, allowing attackers to potentially trick a victim into visiting a malicious domain.2 min#security
- How I Hacked My College's Online Exam Portal During COVID-19 Quarantine PeriodA stored XSS in the exam portal my college built during lockdown: a kill-switch first, then a fake login form that phished credentials from the portal’s own domain.5 min#security
- How I Hacked Samsung's Tizen OS & LG Electronics Private Project Management InstancesA flaw hackers can use to access Samsung’s and LG Electronics internal bug tracking project management instances running on Jira.1 min#security
- Internet's reading delicaciesInternet's reading delicacies for founders and investors alike.1 min#startups
- No, It’s Not Everyone’s Favorite “Kali Wifi Hacking Tutorial” — Impersonating Anyone In CollegeMy college’s i-ON WiFi logged you in by MAC address alone, so sniffing one and wearing it made you anyone on campus. No credentials needed.4 min#security
- How A Bad Implementation Can Allow Anyone To Hijack Every My Campus Days AccountA forgotten password on my first day at college led to a reset feature that set every account’s username and password to its Admission ID.4 min#security
- Passing IIT Bombay’s FOSSEE Quiz at 3 AM, and Walking AwayA fellowship quiz that leaked its own answers through Python assert errors, a 3 AM script that passed it, and why I never submitted the screening task.5 min#security
- OS Command Injection on Node.JS Jison moduleDiscovering an OS command injection vulnerability in Jison parser ports that allows arbitrary shell command execution.2 min#security